Showing posts with label PCI Security Standards Council. Show all posts


Approved PIN Transaction Security

Please review the legal conditions and restrictions regarding PCI PTS approval contained in the Payment Card Industry PIN Transaction Security Testing and Approval Program Guide (PDF 2.25 MB).


  Filter PTS Vendors by Company Name:

  Show All   # A B C D E F G H I J K L M N O P Q R S T U V W X Y Z


  Filter PTS by:


Alphabetical

Expiry Date


Search PTS by Vendor name, Product name, Approval number:


Export To ExcelPrintable Format
Last Update: Apr 21st, 2010
4 Vendors, 6 Devices


Hangzhou Sunyard Technology Co Ltd
PTS Identifier1Approval

Number2
VersionProduct

Type3
Expiry

Date4
P80


hardware # : HD-D-0x-S-0x
firmware # : BIOS-V001
applic # : USR-V001
4-400432.xPED30 Apr 2017
S180


hardware # : HD-V1.01
firmware # : BIOS-V1.01
applic # : USR-V1.00
4-400472.xPED30 Apr 2017
HomeATM
PTS Identifier1Approval

Number2
VersionProduct

Type3
Expiry

Date4
SafeTPIN


hardware # : 3.0
firmware # : 1.02
applic # : 
4-400352.xPED30 Apr 2017
Hypercom
PTS Identifier1Approval

Number2
VersionProduct

Type3
Expiry

Date4
L4150 and SKP4150


hardware # : 0220xx and 0240xx
firmware # : FPE 5.P.0xx,

FPE 5.P.1xx

and HYCSKP_2.0x
applic # : 
4-600282.xPED30 Apr 2017
L4150 


hardware # : 0220xx
firmware # : FPE 5.P.0xx,

FPE 5.P.1xx
applic # : 
4-600282.xPED30 Apr 2017
Hypercom
PTS Identifier1Approval

Number2
VersionProduct

Type3
Expiry

Date4
T42xx, M42xx


hardware # : 0630xx
firmware # : 5.0.x xxxxxxxx
applic # : 
4-600362.xPED30 Apr 2017


Top of Page
Enhanced by Zemanta

Posted by John B. Frank Friday, June 18, 2010 0 comments


LAS VEGAS, May 20 /PRNewswire/ -- eCommLink, a leading value-added prepaid debit card processor, has announced its status as a participating organization with the PCI Security Standards Council.  The affiliation unites the company with the other industry leaders and holds eCommLink to criterion beyond the basic PCI requirements.
"Security and compliance within our organization and our domestic and international clients is our highest priority," states eCommLink CEO, Ennio Ponzetto.  "This is evidenced by our increased investment in these areas.  Our dedicated compliance officer ensures our adherence to industry policies, procedures and practices, and we recently hired a senior information security engineer to enforce our data security standards at an even higher level."  
Victor Newsom, Chief Operations Officer and Executive Vice President of Business Development concurs.  "eCommLink is committed to providing the most secure prepaid processing environment for our clients and their cardholders.  Membership and participation in this internationally recognized organization impels us to maintain the highest standards and follow industry best practices to ensure customer security and satisfaction."
The company has been independently audited for compliance with the Payment Card Industry Data Security Standard (PCI DSS) and holds Level 1.2 certification.  
About eCommLink, Inc.
eCommLink, Inc. (www.ecommlink.com) enables program managers and financial institutions to maximize revenue from their prepaid debit programs.  The Company's flexible prepaid processing platform, innovative features and industry experience allows clients to create customized prepaid programs for their specific markets while ensuring quality, security and time to market.  eCommLink supports the full array of prepaid debit programs, including general spend, payroll, teen, gift, travel, government and loyalty cards.
About the PCI Security Standards Council
The PCI Security Standards Council provides a variety of tools, questionnaires, guidance, FAQs, training resources and other materials and information to assist organizations seeking to achieve compliance with its standards. The PCI DSS is a multifaceted security standard that includes requirements for security management, policies, procedures, network architecture, software design and other critical protective measures. This comprehensive standard is intended to help organizations proactively protect customer account data.
SOURCE eCommLink, Inc.
Reblog this post [with Zemanta]

Posted by John B. Frank Thursday, May 20, 2010 0 comments


LAS VEGAS, May 20 /PRNewswire/ -- eCommLink, a leading value-added prepaid debit card processor, has announced its status as a participating organization with the PCI Security Standards Council.  The affiliation unites the company with the other industry leaders and holds eCommLink to criterion beyond the basic PCI requirements.
"Security and compliance within our organization and our domestic and international clients is our highest priority," states eCommLink CEO, Ennio Ponzetto.  "This is evidenced by our increased investment in these areas.  Our dedicated compliance officer ensures our adherence to industry policies, procedures and practices, and we recently hired a senior information security engineer to enforce our data security standards at an even higher level."  
Victor Newsom, Chief Operations Officer and Executive Vice President of Business Development concurs.  "eCommLink is committed to providing the most secure prepaid processing environment for our clients and their cardholders.  Membership and participation in this internationally recognized organization impels us to maintain the highest standards and follow industry best practices to ensure customer security and satisfaction."
The company has been independently audited for compliance with the Payment Card Industry Data Security Standard (PCI DSS) and holds Level 1.2 certification.  
About eCommLink, Inc.
eCommLink, Inc. (www.ecommlink.com) enables program managers and financial institutions to maximize revenue from their prepaid debit programs.  The Company's flexible prepaid processing platform, innovative features and industry experience allows clients to create customized prepaid programs for their specific markets while ensuring quality, security and time to market.  eCommLink supports the full array of prepaid debit programs, including general spend, payroll, teen, gift, travel, government and loyalty cards.
About the PCI Security Standards Council
The PCI Security Standards Council provides a variety of tools, questionnaires, guidance, FAQs, training resources and other materials and information to assist organizations seeking to achieve compliance with its standards. The PCI DSS is a multifaceted security standard that includes requirements for security management, policies, procedures, network architecture, software design and other critical protective measures. This comprehensive standard is intended to help organizations proactively protect customer account data.
SOURCE eCommLink, Inc.
Reblog this post [with Zemanta]

Posted by John B. Frank 0 comments


http://www.comdata.com

Comdata Corporation Supports PCI Security Standards Council as Participating Organization

Comdata works with key standards setting body to protect payment cardholder data
BRENTWOOD, Tenn.--(BUSINESS WIRE)--Comdata Corporation, provider of the new Smart Solutions suite of point-of-sale systems for travel plazas and convenience stores, announced today its support of the PCI Security Standards Council. As a participating organization, Comdata works with the Council to evolve the PCI Data Security Standard (DSS) and other payment card data protection standards.
“Data protection is critical to Comdata, and we are honored to be an active participant in shaping the standards that will ensure safe business practices”
The PCI DSS, endorsed by American Express, Discover Financial Services, JCB International, MasterCard Worldwide and Visa Inc., requires merchants and service providers that store, process or transmit customer payment card data to adhere to information security controls and processes that ensure data integrity. More information on the council and the standard can be found atwww.pcisecuritystandards.org.
As a participating organization, Comdata has access to the latest payment card security standards from the Council, is able to provide feedback on the standards and is part of a growing community that includes more than 500 organizations. In an era of increasingly sophisticated attacks on systems, adhering to the PCI DSS represents an entity’s best protection against data criminals. By serving as a participating organization, Comdata is adding its voice to the process.
“The PCI Security Standards Council is committed to helping everyone involved in the payment chain protect consumer payment data,” said Bob Russo, general manager of the PCI Security Standards Council. “By participating in the standards setting process, Comdata demonstrates they are playing an active part in this important end goal.”
“Data protection is critical to Comdata, and we are honored to be an active participant in shaping the standards that will ensure safe business practices,” said Joseph Daly, executive vice president of operations for Comdata. “The PCI Security Standards Council is a driving force for payment policy, and they share our commitment to providing the highest standards of data security for our customers.”
About PCI Security Standards Council
The mission of the PCI Security Standards Council is to enhance payment account security by driving education and awareness of PCI security standards. For more information, please visit www.pcisecuritystandards.org.
About Comdata Corporation
Comdata Corporation is a leading provider of truck stop and convenience store point-of-sale (POS) systems and a business-to-business provider of innovative electronic payment solutions. As an issuer and a processor, the company enables more than $23 billion in fleet card, credit card, paycard and virtual card transactions annually. Over 1.8 million Comdata cards are issued annually, and active cards at any given time total approximately 1.5 million. With state-of-the-art technology and redundancy, Comdata captures and reports detailed transaction data, empowering its customers to analyze their spending patterns in order to gain unprecedented control of their expenses. Other Comdata solutions include regulatory compliance programs and receivables financing options. Comdata provides solutions to over 25,000 customers in four primary industries: fleet, aviation, construction and retail/hospitality. Founded in 1969 and headquartered in Brentwood, Tennessee with more than 1,000 employees in the United States and Canada, Comdata is a wholly-owned subsidiary of Ceridian Corporation.
About Ceridian
Ceridian is a leading global business services company that provides reality-based KnowHow to take the guesswork out of impacting your organization’s bottom line. From human resources and benefits to productivity and payroll services, we help organizations maximize their human, financial and technology resources. As a leader in payroll outsourcing, gift cards and corporate expense management, we're the driving force in payment innovation. Whether we're partnering with you to save money, grow your business, enhance operations or minimize financial risks we provide the insights and solutions that ensure your success.

Contacts

Comdata Corporation

Trisha Torrado, 615-376-8601

ttorrado@comdata.com

or

PCI Security Standards Council

Ella Nevill, 781-876-6248

enevill@pcisecuritystandards.org
Permalink: http://www.businesswire.com/news/home/20100329005091/en/Comdata-Corporation-Supports-PCI-Security-Standards-Council


Reblog this post [with Zemanta]

Posted by John B. Frank Monday, March 29, 2010 0 comments


http://www.comdata.com

Comdata Corporation Supports PCI Security Standards Council as Participating Organization

Comdata works with key standards setting body to protect payment cardholder data
BRENTWOOD, Tenn.--(BUSINESS WIRE)--Comdata Corporation, provider of the new Smart Solutions suite of point-of-sale systems for travel plazas and convenience stores, announced today its support of the PCI Security Standards Council. As a participating organization, Comdata works with the Council to evolve the PCI Data Security Standard (DSS) and other payment card data protection standards.
“Data protection is critical to Comdata, and we are honored to be an active participant in shaping the standards that will ensure safe business practices”
The PCI DSS, endorsed by American Express, Discover Financial Services, JCB International, MasterCard Worldwide and Visa Inc., requires merchants and service providers that store, process or transmit customer payment card data to adhere to information security controls and processes that ensure data integrity. More information on the council and the standard can be found atwww.pcisecuritystandards.org.
As a participating organization, Comdata has access to the latest payment card security standards from the Council, is able to provide feedback on the standards and is part of a growing community that includes more than 500 organizations. In an era of increasingly sophisticated attacks on systems, adhering to the PCI DSS represents an entity’s best protection against data criminals. By serving as a participating organization, Comdata is adding its voice to the process.
“The PCI Security Standards Council is committed to helping everyone involved in the payment chain protect consumer payment data,” said Bob Russo, general manager of the PCI Security Standards Council. “By participating in the standards setting process, Comdata demonstrates they are playing an active part in this important end goal.”
“Data protection is critical to Comdata, and we are honored to be an active participant in shaping the standards that will ensure safe business practices,” said Joseph Daly, executive vice president of operations for Comdata. “The PCI Security Standards Council is a driving force for payment policy, and they share our commitment to providing the highest standards of data security for our customers.”
About PCI Security Standards Council
The mission of the PCI Security Standards Council is to enhance payment account security by driving education and awareness of PCI security standards. For more information, please visit www.pcisecuritystandards.org.
About Comdata Corporation
Comdata Corporation is a leading provider of truck stop and convenience store point-of-sale (POS) systems and a business-to-business provider of innovative electronic payment solutions. As an issuer and a processor, the company enables more than $23 billion in fleet card, credit card, paycard and virtual card transactions annually. Over 1.8 million Comdata cards are issued annually, and active cards at any given time total approximately 1.5 million. With state-of-the-art technology and redundancy, Comdata captures and reports detailed transaction data, empowering its customers to analyze their spending patterns in order to gain unprecedented control of their expenses. Other Comdata solutions include regulatory compliance programs and receivables financing options. Comdata provides solutions to over 25,000 customers in four primary industries: fleet, aviation, construction and retail/hospitality. Founded in 1969 and headquartered in Brentwood, Tennessee with more than 1,000 employees in the United States and Canada, Comdata is a wholly-owned subsidiary of Ceridian Corporation.
About Ceridian
Ceridian is a leading global business services company that provides reality-based KnowHow to take the guesswork out of impacting your organization’s bottom line. From human resources and benefits to productivity and payroll services, we help organizations maximize their human, financial and technology resources. As a leader in payroll outsourcing, gift cards and corporate expense management, we're the driving force in payment innovation. Whether we're partnering with you to save money, grow your business, enhance operations or minimize financial risks we provide the insights and solutions that ensure your success.

Contacts

Comdata Corporation

Trisha Torrado, 615-376-8601

ttorrado@comdata.com

or

PCI Security Standards Council

Ella Nevill, 781-876-6248

enevill@pcisecuritystandards.org
Permalink: http://www.businesswire.com/news/home/20100329005091/en/Comdata-Corporation-Supports-PCI-Security-Standards-Council


Reblog this post [with Zemanta]

Posted by John B. Frank 0 comments

NEW YORK, Feb 08, 2010 (BUSINESS WIRE) -- Translations.com, the world's largest privately held provider of translation services and language management technologies, today announced the successful localization of www.PCISecurityStandards.org into French, Spanish, Chinese, Japanese, Portuguese, Italian, and German.


Founded in 2006 by American Express, Discover Financial Services, JCB International, MasterCard Worldwide, and Visa Inc., the PCI Security Standards Council is responsible for the development, management, education, and awareness of the PCI Data Security Standards, which are designed to ensure the security of cardholder data worldwide. The PCI Security Standards Council has over 600 Participating Organization companies worldwide. Bob Russo, general manager of the PCI Security Standards Council, explained, "As a global organization focused on securing payment card data, it is critical we provide our stakeholders worldwide with the resources they need to meet this goal, in their own language."


Translations.com's GlobalLink(TM) technology offers companies both hosted and installed options for launching and automatically maintaining translated websites with minimal IT involvement. By combining GlobalLink OneLink with Translations.com's language services, PCI was able to localize its website and related documents into 8 languages in only 2 months with a completely hosted solution. When PCI makes updates to the English website in the future, GlobalLink will automatically detect and route new content to Translations.com for localization by professional human translators, then insert the completed translations back into the proper location on the global websites.


"As we continue to develop PCI Security Standards and produce new resources for our stakeholders, it was critical for us to partner with a company who could help us manage our dynamic multilingual site in a cost effective and timely manner," added Russo.


Translations.com CEO Phil Shawe said, "By making their website and standards information accessible to stakeholders in a range of languages, the PCI Security Standards Council has made a significant step forward in its mission to secure payment card data worldwide. We applaud the Council for its efforts and look forward to supporting their ongoing global initiatives for years to come."


About PCI Security Standards Council


The mission of the PCI Security Standards Council is to enhance payment account security by driving education and awareness of the PCI Data Security Standard and other standards that increase payment data security.


The PCI Security Standards Council was formed by the major payment card brands American Express, Discover Financial Services, JCB International, MasterCard Worldwide and Visa Inc. to provide a transparent forum in which all stakeholders can provide input into the ongoing development, enhancement and dissemination of the PCI Data Security Standard (DSS), PIN Transaction Security Requirements (PTS) and the Payment Application Data Security Standard (PA-DSS). Merchants, banks, processors and other vendors are encouraged to join as participating organizations.


About Translations.com


Translations.com is a leading provider of software, website, and enterprise-wide localization services, as well as localization-related technology products. Translations.com solutions allow customers to conduct business more effectively in international markets. The company has a global presence on four continents and services a variety of clients with dedicated practice groups for every major industry. Translations.com is part of the TransPerfect family of companies. For more information, please visit www.translations.com or www.transperfect.com.


SOURCE: Translations.com Translations.com

Jacquelyn Lane, +1 619.696.9000

mediainquiry@translations.com


Posted by John B. Frank Monday, February 8, 2010 0 comments

Data Security Summit Spring 2009 - Hosted by ProPay
March 18th -19th Cliff Lodge at Snowbird Resort, Little Cottonwood Canyon, Utah


I posted about this a month ago (Propay Security Summit) but as the event quickly approaches, (March 18th and 19th) I thought I'd do a refresher post. ProPay has put together quite an impressive lineup of featured speakers. HomeATM's Chariman and CEO, Ken Mages will be attending the event, which takes place at the Snowbird Resort in Salt Lake City, Utah.

FOR IMMEDIATE RELEASE

ProPay Gathers Industry Experts to Address Payment Industry Trends at 2009 Data Security Summit

Bob Russo, Chris and Dr. Heather Mark, and Michael Dortch among featured speakers to discuss PCI compliance, risk mitigation and data security

Orem, Utah -February 9, 2009- ProPay is gathering the brightest minds in the digital transaction industry to educate attendees about the latest trends and best practices to protect sensitive customer data at the 2009 Data Security Summit on March 18-19, 2009, at the Snowbird Resort in Salt Lake City, Utah.

Headlining the Summit’s speakers are Bob Russo, General Manager, PCI Security Standards Council; Chris and Dr. Heather Mark, Founders, Society of Payment Security Professionals; and Michael Dortch, former Senior Research Analyst, Aberbeen Group. Speakers will address the latest in PCI compliance, risk mitigation, security, and other relevant topics pertaining to the payment industry.

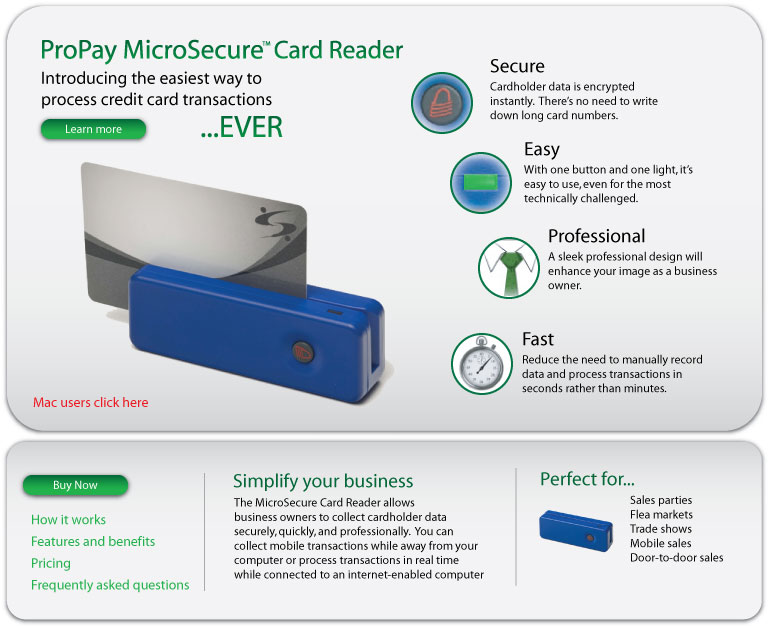
Editor's Note: See if you can find the common denominator between what HomeATM is doing with their SwipePIN PED device and what ProPay is doing with it's MicroSecure® Magnetic Stripe Card Reader. If you said Hardware vs. Software in order to protect Cardholder data then you've been paying attention!

Below the graphic there's a quick Bio on the featured speakers:


Bob Russo, General Manager, PCI Security Standards Council


Mr. Russo brings more than 25 years of high-tech business management, operations and security experience to the PCI Security Standards Council. Most recently, he served as the vice president of Commercial Sales for Secure Info, a provider of security, risk and compliance services and software. He was also a founder of a number of software and security companies including Network-1 Software & Technology and ATC Security, a security compliance company created to assess compliance of payment industry stakeholders, later acquired by Ambiron LLC.

Chris Mark, Founder, Society of Payment Security Professionals


Chris is an experienced information security professional and recognized payment card industry security expert. Chris is a co-founder of The Aegenis Group and the Society of Payment Security Professionals. From 2007-2009, the Aegenis Group was the worldwide trainer for all Qualified Security Assessors (QSA) and trained over 2,800 QSA. Additionally, the company contracts with Visa Inc. to conduct PCI related training internationally to merchants and banks. Chris has conducted PCI and payment security training in over 10 countries on 5 different continents.

Dr. Heather Mark, Founder, Society of Payment Security Professionals


Dr. Mark is an experienced information security and privacy professional that is both well known and respected within the Payment Services industry. Prior to joining Halcyon Dr. Mark co-founded a Qualified Security Assessment Company and worked at various technology companies supporting PCI efforts. Dr. Mark helped to develop a variety of assessment methods and practices that assisted companies in achieving compliance in a cost-effective, timely manner.

Michael Dortch, Founder and Managing Editor, DortchOnIT.com


Michael Dortch is Founder and Managing Editor of DortchOnIT.com, and has been an IT industry analyst, consultant, evangelist, speaker, writer, and "information entrepreneur" for more than 30 years, focused on enabling and emerging technologies and their effects on business value. Before starting DortchOnIT.com, Michael was a Senior Research Analyst at Aberdeen Group, and Director of IT Infrastructure Management Strategies and Executive Editor for Robert Frances Group. Michael has worked with IT users and both established and start-up vendors to help them align their strategies with business goals. He has been widely quoted and is a frequent and popular speaker at industry events. He began his career in the 1970s at The Yankee Group after attending the Massachusetts Institute of Technology (M.I.T.). He lives and works in Santa Rosa, CA, approximately an hour north of San Francisco.

John Verdeschi - VP of Sales and Standards - MasterCard Payment System Integrity Group


John Verdeschi is Vice President of Sales and Standards, in the MasterCard Payment System Integrity group. In this role, he is responsible for managing MasterCard's global risk product sales team, the Payment Card Industry (PCI) Data Security Standard and MasterCard SecureCode. Mr. Verdeschi is a member of the PCI Security Standards Council executive committee which is comprised of MasterCard and other leading payment brands. Since joining MasterCard in 1999, Mr. Verdeschi has concentrated on programs which help secure transaction data and manage fraud within the electronic payments channel.

Representatives from the various card brands and payment industry companies, as well as experts from law enforcement agencies and the F.B.I will be on hand to network with attendees and talk about the latest from their businesses and organizations.


"The landscape of the payment industry is ever-changing and the need to educate the market on best practices and the latest technology to protect businesses is essential to the survival of every company,” said Greg Pesci, ProPay Executive Vice President of Business Strategy. “This Summit is a great opportunity to bring experts and non-experts together to educate each other on the trends in the market and the pains customers and businesses are experiencing in regards to digital transactions."

For more information about the 2009 Data Security Summit and how to register, please visit www.propay.com/summit or e-mail Jennifer McClintock at events@propay.com.


About ProPay


Since 1997, ProPay has led the market in providing simple, safe and affordable credit card processing and electronic payment services for businesses ranging from the small, home-based entrepreneur to multi-billion-dollar enterprises.

ProPay understands the unique needs of these businesses and has created merchant services specifically for them. With ProPay, merchants can set up accounts online and begin accepting credit cards without buying special equipment or making long-term commitments or investments. ProPay leads out in educating merchants about how to reduce or eliminate the risk of touching or holding sensitive cardholder data. The company also leads the payments market in the development of secure end-to-end solutions for protecting sensitive data and of alternative payment options that significantly reduce business costs.

ProPay is a privately held company, headquartered in Orem, Utah. For information, visit
www.propay.com/pressroom.


Reblog this post [with Zemanta]

Posted by John B. Frank Friday, March 13, 2009 0 comments

Payments Industry News Blog

Search the PIN Debit Blog by Subject

Kapersky Calls for Mass Adoption of Card Readers

Kapersky Calls for Mass Adoption of Card Readers